The Dept. of Defense Inspector General’s office has dropped a criminal complaint against former CMMC architect Stacy Bostjanick without any explanation, concealing its decision and indicating it would only release information on the matter via FOIA.
The complaint was filed by Oxebridge in July of 2026 and alleged multiple violations of law by Bostjanick, including:
- 18 U.S.C. Section 207(c) – requires a one-year “cooling off” period before a former Executive branch employee may make representational communications with, or appearances before, officers or employees of the executive branch on behalf of a third party with the intent to influence official action. Bostjanick appeared at an event representing Cybersec alongside her DoD replacement, Aaron Bishop.
- 18 U.S.C. Section 207(a)(1) – requires a lifetime ban for any former Executive branch employee if their work included conducting or overseeing administrative matters involving specific parties. Oxebridge argues that Bostjanick performed highly specific acts to benefit the Cyber AB and Cybersec, among others, through her willful suppression of complaints, FOIAs, and other actions that might have restricted those parties.
- 18 U.S.C. Section 208 – governs acts by employees affecting a personal financial interest. Oxebridge argues Bostjanick’s actions while at the DoD were conducted to benefit parties whom she then intended to work with once leaving employment. If she negotiated her employment at Cybersec while at DoD, Oxebridge argues this is a violation. Oxebridge also argues that by Bostjanick used her public office for private gain by co-marketing Cybersec Investments while in her official DoD capacity.
- 5 C.F.R. Part 2635 – defines Standards of Ethical Conduct. Oxebridge argues that Bostjanick clearly violated Subpart G (Misuse of Position) and Subpart A (creating the appearance of violating the law or ethical standards, and giving preferential treatment to a private organization).
The IG’s office shut down the matter in mere weeks, suggesting that it performed no investigation at all into Bostjanick.
Bostjanick appears to continue to lobby on behalf of her company without registering as a lobbyist, and has continued to personally benefit from the work she did at DoD.
The DOD Inspector General’s office has come under fire for years for working to cover up wrongdoing by government officials and enabling, rather than curbing, fraud, waste, and abuse. This article by USAF Lt. Col (Ret) Ryan Sweazey reveals this is a feature of the DODIG, not a bug.
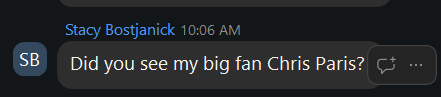
Bostjanick did not take the news gracefully and instead mocked Oxebridge founder Christopher Paris during a live September 25 Cyber AB call with CMMC assessment bodies.
Bostjanick may not be cleared entirely, however. Oxebridge may still file the FOIA to unmask the DoD’s decision and she may yet be subject to investigation and prosecution through other avenues, as well as civil litigation.